Find
Find the vulnerabilities that actually get exploited
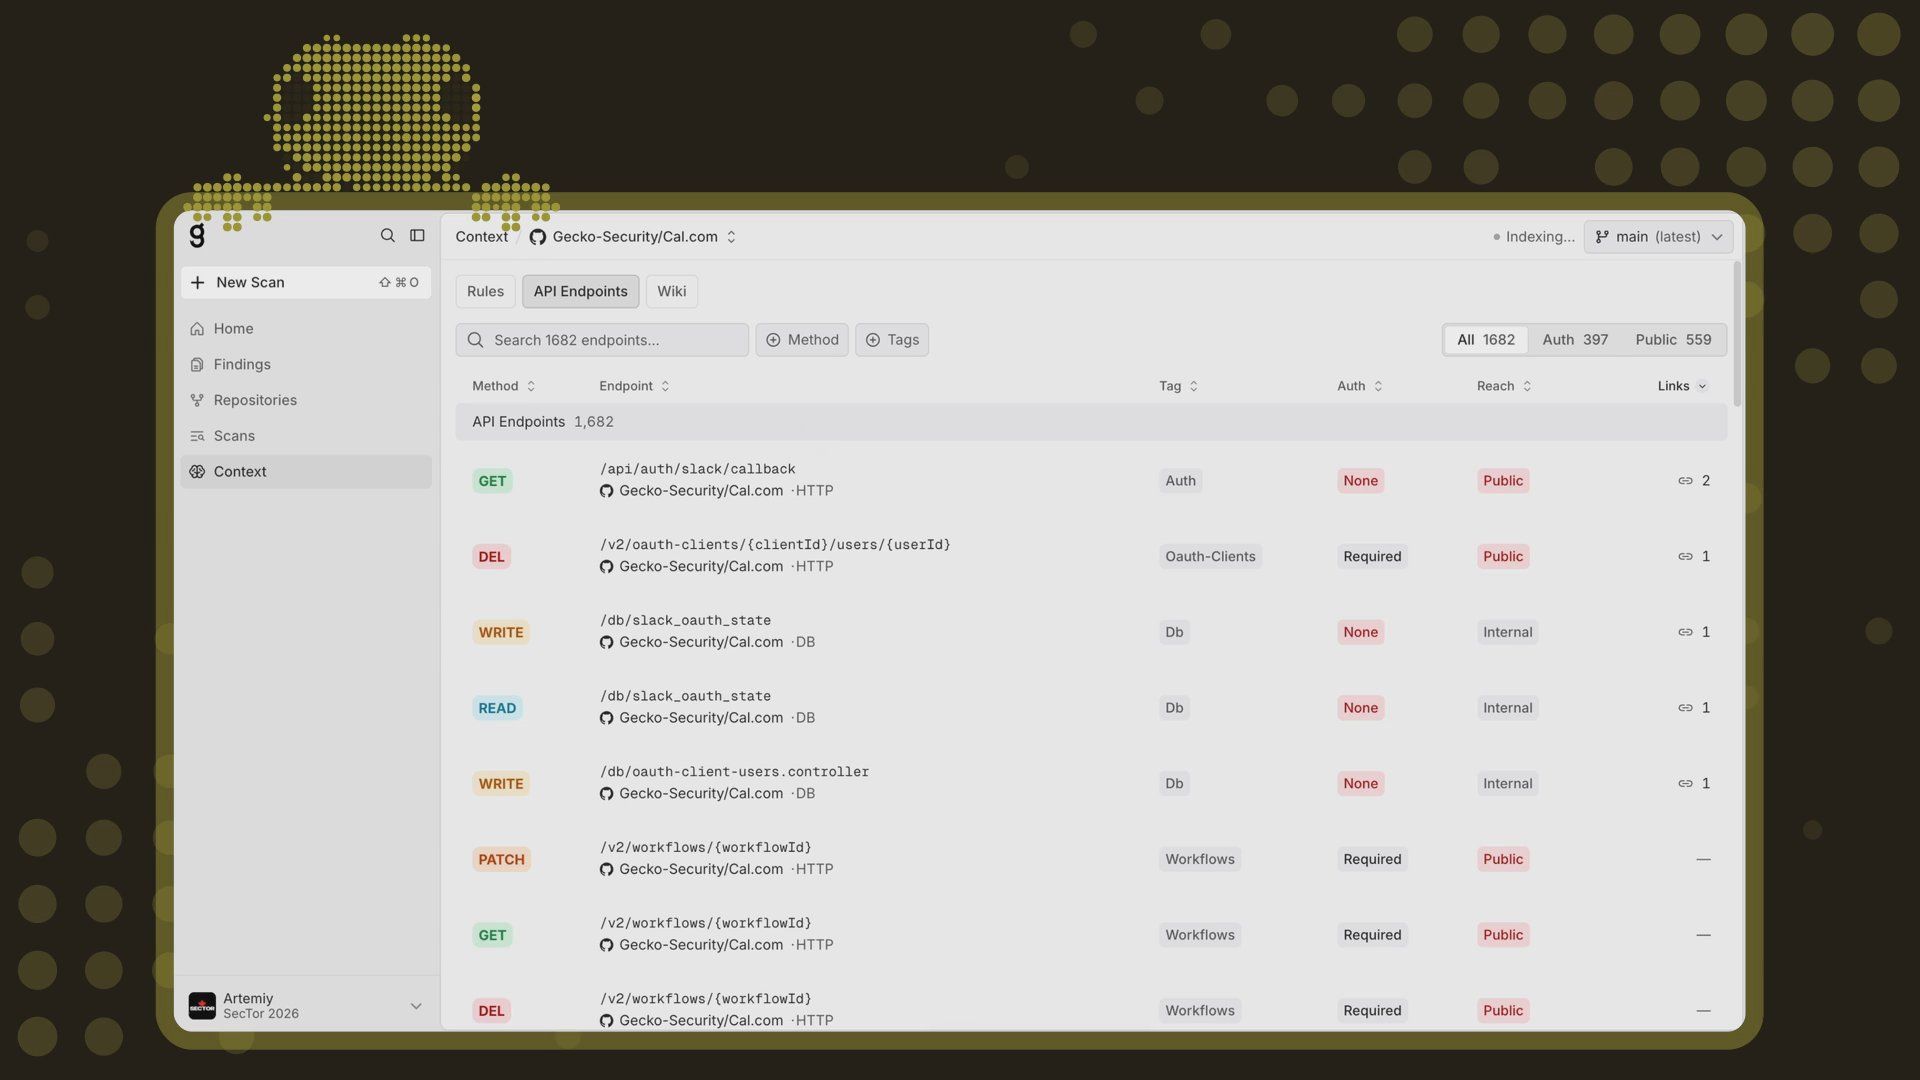
Gecko reads your code, infrastructure and design docs as one system, and finds the logic flaws that live between them.

Gecko reasons across your code, infrastructure and intent to find the vulnerabilities that actually get exploited, prioritize them from the attacker’s perspective, fix the root cause and every variant in one PR, and make sure they never come back.
 Crux
 b.well
 Cal.com
 GoodLabs
 Avora
 Paid.ai
 Guardant Health

“The vulnerabilities that keep CISOs up at night are business logic flaws and multi-step attack chains most tools can’t see. That’s where breaches happen. Gecko is built to find them.”

Jon Raper
CISO, Chevron

“One tool that gives us great results from a full scanning perspective, and every single pull request that goes in, we know is protected.”

Keith Williams
Head of Engineering, Cal.com

“Gecko found business logic vulnerabilities we’ve only ever been able to get from manual code reviews, and the false positive rate is the lowest we’ve seen from any scanner”

MD of Security
F500 Financial Institution
100 alerts, one cause. Gecko fixes the decision upstream,
so you can say goodbye for good.
Find
Gecko reads your code, infrastructure and design docs as one system, and finds the logic flaws that live between them.
Prioritize
Attackers chain small bugs into big breaches. Gecko ranks your findings by the attack path they form, so the lows that add up to a takeover outrank a critical nobody can reach.
Fix
One PR fixes the design decision behind a finding, and every variant it created, in your codebase’s style.
Prevent
Every fix becomes a guardrail, enforced on every PR and inside the AI agents writing your code.
MTTR tells you how fast you closed a ticket. It doesn’t tell you the flaw stayed gone. Gecko fixes vulnerability classes at the root, so the number that keeps falling is the one that measures real progress.
Integrations
Gecko connects to your repos, pipelines, and trackers with native connectors for Claude, Codex, and any MCP server.



The latest news, technologies, and resources from our team.
How Cal.com consolidated noisy security tooling into one continuous, context-aware pull request security program with Gecko.

Gecko Security
Authorization bypass in n8n’s dynamic-credentials OAuth endpoints allows any authenticated user to operate on another user’s OAuth credential by supplying its ID, enabling unauthorized OAuth rebinding and revocation.

Artemiy Malyshau
An IDOR vulnerability in n8n’s public variables API allows authenticated users to read project variables outside their authorized scope, exposing secrets across project boundaries.
Artemiy Malyshau
Learn API scanning for automated security testing. Find vulnerabilities from broken authentication to business logic flaws in your endpoints.
Artemiy Malyshau
A complete guide to automated pentest tools and best practices. Learn what works, what doesn’t, and how to implement continuous security testing.
Artemiy Malyshau
Compare the best AI-powered application security testing tools. Find which tools detect business logic flaws and broken access control.
Artemiy Malyshau
What people ask before they point Gecko at a repo.
The fastest way to evaluate Gecko is to point it at a real repository. First findings typically arrive within the hour.